 HilSecLtd
Leadership
A leadership perspective on why HilSec exists, how we think about security, and where we're taking the company next.
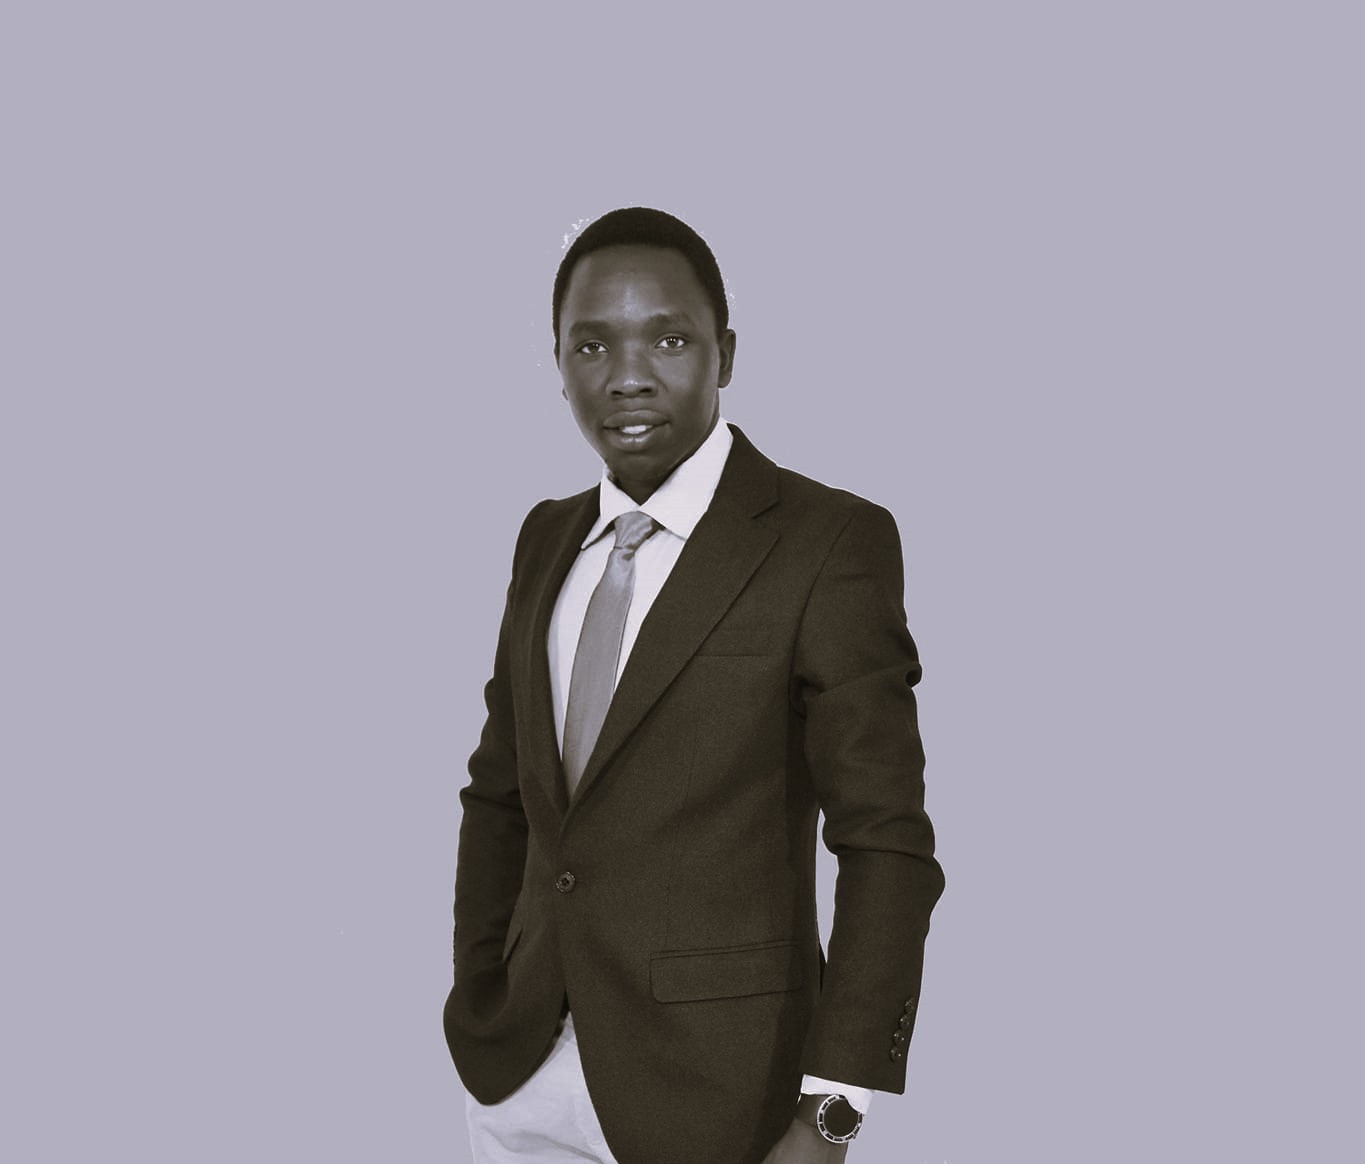
A Message from Our CEO
"We started HilSec because too many organizations - especially across Africa - were being asked to choose between affordability and world-class protection. That shouldn't be a choice. Our mission is to bring enterprise-grade cybersecurity, delivered with the same rigor and integrity you'd expect from any global leader, to every client we serve, regardless of size or sector."
Tim Murkomen
Chief Executive Officer, HilSec
"Because someone has to keep the Internet honest."
IT Security · DevSecOps · Software Development · Risk · GRC · IT Leadership · Advocate of Tech-Driven Sustainable Development in Africa · Author
Published Articles
Research Publications
Research Citations
Professional Network
Founder & CEO, HilSec Ltd · 2020 - Present
Five chapters of building HilSec from a single idea into a trusted regional cybersecurity partner. Scroll down to follow the road.
Founded HilSec on a simple conviction: organizations shouldn't have to choose between affordability and enterprise-grade protection.
Stood up HilSec's core practice - security assessments, GRC advisory, and penetration testing - grounded in certified, hands-on expertise.
Expanded into managed security operations and blockchain security, extending engagements to enterprise and government clients across the region.
Launched ThreatRadar, SecureVault, and AutoSecComply - turning years of client engagements into reusable, AI-assisted security products.
Today, still leading from the front - pairing human expertise with intelligent automation to keep HilSec's clients a step ahead.
Our Direction
Our vision is simple to state and hard to earn: become the cybersecurity partner that governments, financial institutions, and enterprises across Africa and beyond trust by default - not because of marketing, but because of consistent, verifiable outcomes.
That means investing in our people first. Every engagement, from a single penetration test to a fully managed SOC relationship, is built on the judgment of certified practitioners - supported, not replaced, by automation and AI-assisted tooling. Technology accelerates our team; it doesn't stand in for it.
It also means growing deliberately. We would rather deepen our expertise in the services and industries we already serve well - GRC, cloud security, managed security operations, blockchain security - than spread thin chasing every emerging trend. Sustainable trust is built one well-executed engagement at a time.
Security is not a product you buy once - it's a discipline you practice continuously. At HilSec, we believe the strongest defenses come from pairing experienced human judgment with intelligent automation: people who understand adversary behavior working alongside systems that can watch, correlate, and respond faster than any manual process.
We build on a zero trust mindset - never assuming trust based on network location or a single successful login, and instead verifying identity, device posture, and context continuously. This is not a single tool, but an architectural principle we carry across every engagement, from cloud environments to legacy infrastructure.
Perhaps most importantly, we favor proactive security over reactive firefighting. Threat hunting, tabletop exercises, and continuous risk assessment matter as much as incident response, because the organizations that fare best are the ones that find their weaknesses before an adversary does.
A track record built on continuous learning, hands-on practice, and formal recognition from the industry.
Thought Leadership
A selection of Tim's writing on cybersecurity, DevSecOps, GRC, and technology leadership, published on Medium. Filter by topic below.
Off the Record
Keep Exploring
Join the team building the next generation of cybersecurity defenders.
View Careers